Devices provisioned or redeployed
Windows, macOS, ChromeOS, and mobileZachary Woo · San Francisco Bay Area
Security-Aware IT Support Professional
Endpoint Deployment & Troubleshooting · IAM · Security-Aware Operations
I bring production experience in cross-platform endpoint support, Windows deployment, and identity administration. My work combines practical troubleshooting, security-aware configuration, validation before handoff, and clear documentation.
B.S. Software EngineeringCompTIA Security+Google Cybersecurity Certificate
Jira tickets resolved or closed
Final confirmed closed/resolved total; historical backlog reduced from approximately 160-180 to a low of 32.Employees onboarded
Enterprise password manager adoptionDigital-safety training attendees
Historical session; created and co-delivered with two co-presentersProfessional experience
Real IT work, measured by service and follow-through.
My strongest experience comes from supporting real users, endpoints, accounts, and operational priorities across a multi-site environment.
Completed role
IT Technician
Futures Explored, Inc.
- Tenure
- April 2026 - October 2026
- Environment
- Multi-site nonprofit IT
- Primary scope
- Endpoints, users, IAM, helpdesk
01
Cross-platform endpoint lifecycle
Provisioned and redeployed 63+ Windows, macOS, ChromeOS, mobile, and shared-use devices across multiple locations, including Entra joins, software configuration, MDM verification, inventory updates, and user handoff.
02
Helpdesk operations
Closed or resolved 301 Jira tickets; previously reduced the helpdesk backlog from approximately 160-180 tickets to a low of 32.
03
Windows deployment and standardization
Completed an OSDCloud Windows 11 staff deployment pilot with approximately 23-30 minutes of technician hands-on effort, validating Entra join, authentication, encryption, endpoint health, updates, and employee handoff; developed repeatable deployment and USB-build SOPs.
04
Shared endpoint security
Completed two Windows 11 shared-workstation builds with separate administrative and standard-user access, browser and application restrictions, and usability checks. Tested AI-assisted PowerShell automation against the manual baseline and refined validation and rollback guidance. Broader pilot configuration remained a separate phase.
05
IAM and credential operations
Drove enterprise password-manager onboarding for 26 employees with recovery, secure sharing, migration guidance, and legacy-data cleanup. Administered Google Workspace, Microsoft 365, and Entra account lifecycle, licensing, groups, and authentication support.
06
Security awareness and documentation
Created, coordinated, and co-delivered digital-safety training to approximately 40-60 participants with two co-presenters. Delivered final-week participant instruction with live Q&A, maintained class information, and documented staff, shared-workstation, and deployment-media procedures.
07
Structured troubleshooting
Restored Windows PE SSD detection during an OSDCloud staff deployment through manufacturer Intel RST driver loading and USB path troubleshooting. Separately diagnosed a driver-package hash mismatch and tested a temporary local correction. Reduced observed CPU use from approximately 95% to 20% and investigated BitLocker recovery evidence.
08
Infrastructure and endpoint response
Worked with the IT manager to wire 14 public-use computers for Ethernet and establish NAS access for 14 endpoints, including seven configured directly. Restored printing across three Windows endpoints and Yealink/RingCentral service through diagnostics, vendor coordination, and SOPs. Remediated potentially unwanted software through isolation, full and offline antivirus scanning, and clean recovery.
09
Hardware fault isolation
Diagnosed and stabilized two lab laptops through external-peripheral testing, BIOS diagnostics, power isolation, RAM reseating, and repeat boot checks. Validated hardware readiness across four lab systems while keeping short-term stability distinct from a permanent repair.
10
Secure data and operational handoff
Completed off-network antivirus screening of backup data and deployment media, then transferred the scanned backup folder to network storage. Documented approved software, maintenance rollback, remaining deployment tasks, and validation criteria for technical continuity.
Professional experience
Tech Support
Bay Alarm Company · Mar–Apr 2026
Troubleshot alarm, access-control, CCTV, and IP-connected security system issues using remote programming tools, service logs, documentation, and defined escalation paths.
Community experience
Volunteer IT Support
St. Raymond Catholic Church · Jan–Mar 2026
Troubleshot public-facing AV and livestream systems, restricted unauthorized wireless access, validated changes, and documented baseline configurations and operational risk.
Software & Product Delivery
From requirements to a verified release.
A supporting case study in product ownership, quality assurance, technical documentation, and controlled release delivery. My production IT experience remains the foundation.
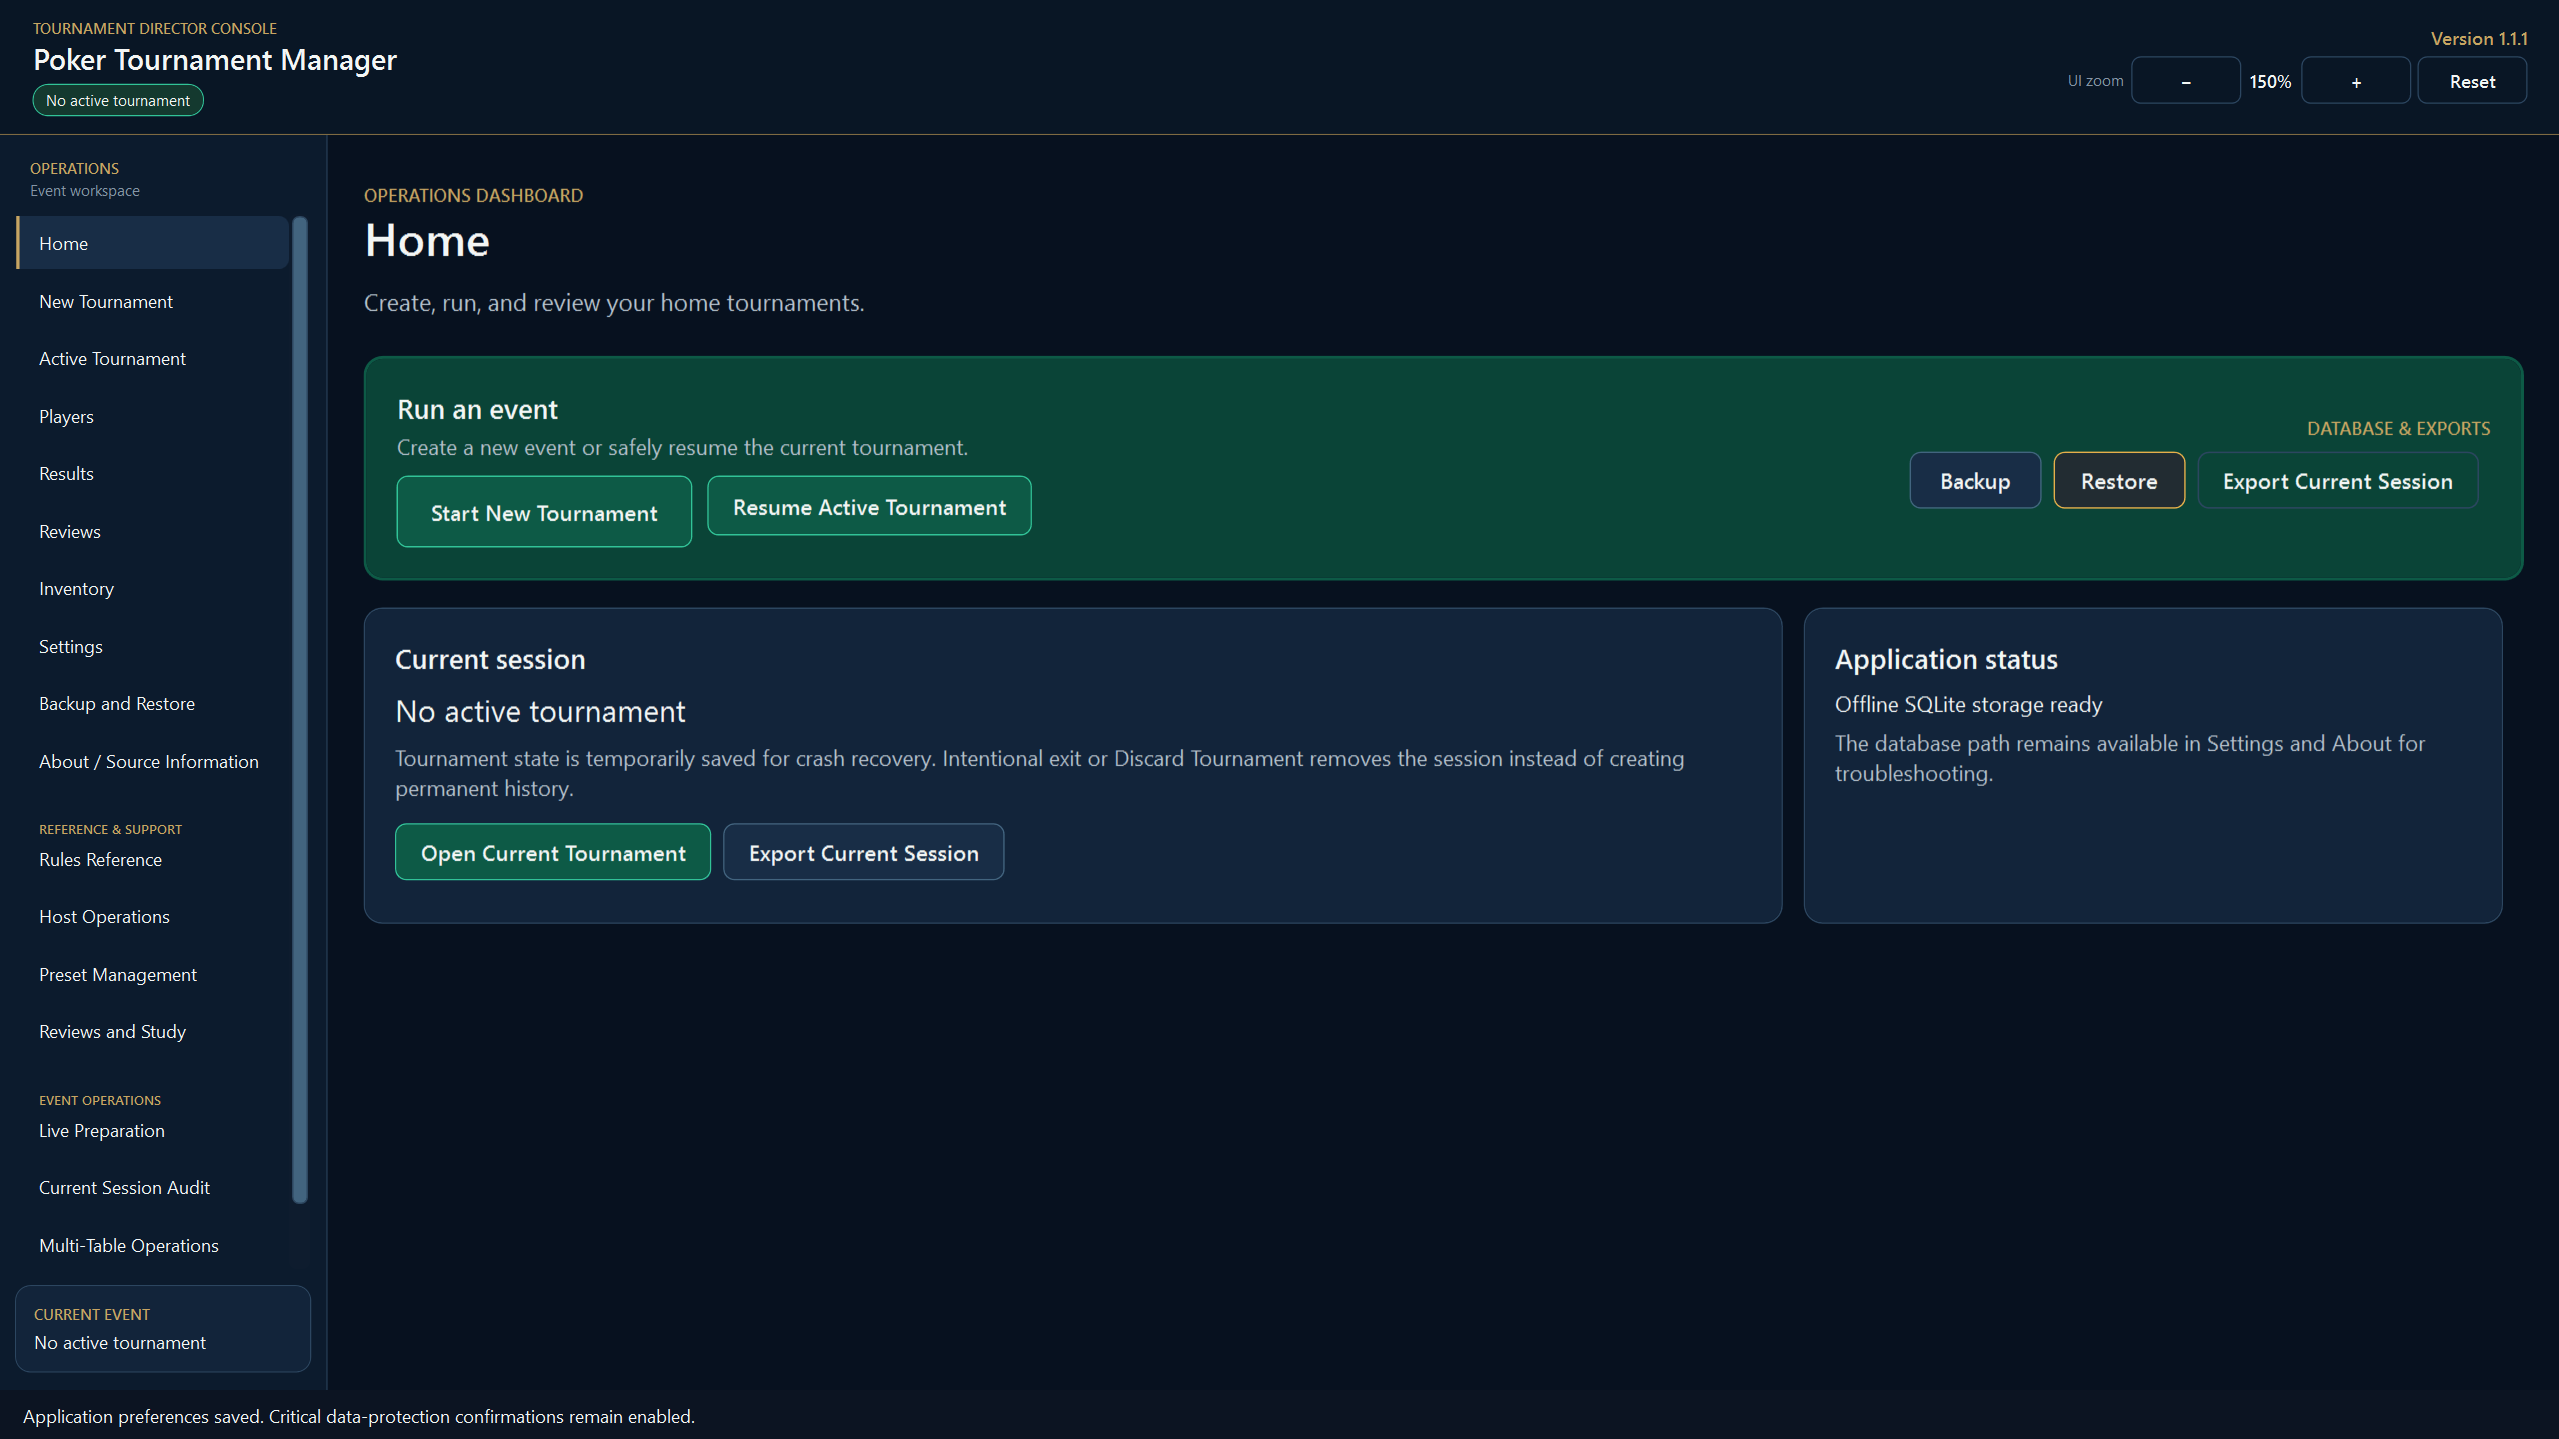
Version 1.1.1Product & Release Engineering
Poker Tournament Manager
Product Owner & Release Lead
Product ownership, UX-informed requirements, physical QA, defect triage, and release management for a validated offline Windows tournament-operations application.
Evidence: v1.1.1 · 274 automated tests · 0 failures · physical packaged-build QA
- Product Management
- Release Management
- Quality Assurance
- Technical Documentation
- C#
- WPF
- .NET 10
- SQLite
View Case StudyDedicated project page · Opens in this tab
Selected projects
Labs that reinforce production-relevant skills.
Each project focuses on implementation, validation, and honest limits. The labs support my professional experience, not substitute for it.
01Technical case study
Active Directory Domain Deployment & RBAC
Built an isolated Windows domain to demonstrate identity administration, role-based access, and least-privilege validation.
- Windows Server 2022
- Windows 10
- AD DS
- DNS
- VirtualBox
Objective
Deploy a functional Active Directory environment and enforce different access levels for IT, HR, and Finance users.
What I implemented
Configured domain services and DNS, created an OU hierarchy, added users and security groups, joined a Windows 10 client, and assigned access through group membership rather than direct user permissions.
How I validated it
Tested the shared resource as representative users. HR and Finance accounts were denied write access, while the IT administrator group retained full file operations.
Security relevance
Demonstrates foundational IAM, RBAC, permission inheritance, domain authentication, and least-privilege thinking.
Limitations & lessons
Single-domain home lab with no Group Policy deployment, centralized logging, network segmentation, or enterprise-scale lifecycle automation.
02Technical case study
Wazuh SIEM Incident Response
Investigated correlated Linux authentication activity, mapped observed behavior, and documented the response as a concise incident report.
- Wazuh SIEM
- Ubuntu Linux
- SSH
- PAM
- sudo
- MITRE ATT&CK
Objective
Use centralized alerting to detect and analyze repeated SSH authentication failures and related privilege activity.
What I implemented
Reviewed Wazuh alerts across SSH, PAM, and sudo sources, correlated repeated failures, reconstructed the event sequence, and mapped observed behavior to password guessing and SSH techniques.
How I validated it
Checked for successful logins, unauthorized account creation, privilege escalation, and follow-on alerts. No successful unauthorized authentication or privilege escalation was observed.
Security relevance
Shows alert triage, timeline analysis, evidence-based scoping, ATT&CK mapping, and careful incident documentation.
Limitations & lessons
Controlled home-lab activity with a narrow Linux endpoint scope. It does not represent production SOC ownership or enterprise incident authority.
03Technical case study
SSH Brute-Force Detection & Mitigation
Detected a simulated authentication attack in native Linux logs, reconstructed its timeline, and validated automated blocking.
- Ubuntu Linux
- OpenSSH
- auth.log
- Bash
- fail2ban
Objective
Detect repeated SSH failures, identify the source pattern, reconstruct the event timeline, and reduce repeated login attempts.
What I implemented
Filtered authentication logs, counted failures by source, separated remote SSH activity from local PAM events, and configured fail2ban to respond to repeated attempts.
How I validated it
Repeated the simulation and confirmed that fail2ban banned the source after the configured threshold and refused subsequent connections.
Security relevance
Demonstrates command-line log analysis, signal validation, automated containment, and verification after a control change.
Limitations & lessons
A small, simulated environment. Production controls would also include key-based authentication, MFA where supported, centralized monitoring, and formal change management.
04Technical case study
Secure Router Provisioning & Hardening
Reprovisioned a previously used consumer router for a local-only workload while documenting security trade-offs and residual risk.
- ASUS Router
- WPA3
- Protected Management Frames
- Isolated LAN
Objective
Create a functional WAN-isolated network while reducing exposure from unknown prior configuration and unnecessary services.
What I implemented
Factory-reset and securely reprovisioned the router, set non-default administrative credentials, separated wireless bands, used WPA3 with protected management frames, and disabled UPnP, cloud services, and remote management.
How I validated it
Verified firmware state, local packet flow, physical WAN isolation, disabled remote services, and successful operation of the intended local workload.
Security relevance
Applies secure baseline configuration, attack-surface reduction, defense in depth, and explicit residual-risk documentation.
Limitations & lessons
Personal lab design without centralized management, automated patching, or enterprise monitoring. Manual firmware maintenance remains necessary.
Detailed sanitized project documentation is available upon request.
Skills & tools
A practical toolkit for reliable, security-aware support.
Organized around the work I can discuss and defend, without arbitrary proficiency scores.
01
Endpoint & systems
- Windows 10/11
- macOS
- ChromeOS
- iOS / iPadOS
- Ubuntu Linux (lab)
- Endpoint provisioning & reprovisioning
- Windows reimaging & recovery
- Windows performance & startup diagnostics
- Entra device joins
- Deployment readiness validation
- MDM verification
- WinDbg · WinRE · DISM · SFC
- BIOS & firmware diagnostics
- Laptop hardware repair
- RAM reseating and power isolation
- Windows PE storage-driver troubleshooting
- Printer IP / DHCP troubleshooting
- Printer queue / driver recovery
- Ethernet & NAS deployment
02
IAM & administration
- Google Workspace
- Google Admin
- Microsoft 365
- Microsoft Admin Center
- Microsoft Entra ID
- IAM & account lifecycle
- Provisioning & termination
- Licensing & password resets
- Account recovery & 2FA
- Groups & security groups
- Entra sign-in log investigation
- OneDrive setup
- MFA · Windows Hello · passkeys
- Enterprise password manager adoption
03
IT operations
- Jira Helpdesk
- RingCentral · Yealink · SIP / VoIP
- Datto
- AssetTiger
- Addigy
- Splashtop
- OneDrive
- Microsoft Teams
- Google Drive
- Google Forms
- Google Sheets
- Asset tracking
- Endpoint auditing
- Multi-site support
- OSDCloud and WinPE deployment
- PowerShell and Winget
- AI-assisted automation validation
- Maintenance validation and rollback
04
Security & documentation
- Microsoft Defender
- Offline antivirus scanning
- PUP remediation
- Wazuh SIEM (lab)
- BitLocker
- Secure deletion
- Encrypted archives
- Endpoint audits
- Least privilege
- Incident documentation
- SOP development
- Security-awareness documentation
- Digital-hygiene training
- Authentication guidance
- Endpoint containment & remediation
- AI acceptable-use guidance
About
Reliable technology support, grounded in practical security.
I am a San Francisco Bay Area IT support professional with a B.S. in Software Engineering and a minor in Justice Studies from San José State University.
My completed Futures Explored experience combines OSDCloud Windows deployment, hardware and software troubleshooting, IAM, Jira operations, security awareness, and technical documentation. I turn findings into repeatable procedures and test AI-assisted automation against working configurations. As I transition into my next IT support role, I am focused on dependable service and deeper endpoint and IAM skills.
- 2025
B.S. Software Engineering
San José State University · Minor in Justice Studies
- DEC 2025
Google Cybersecurity Certificate
Completed all eight courses
- FEB 2026
CompTIA Security+
SY0-701 certified
- 2026
Production IT experience
Endpoint deployment · IAM · troubleshooting · documentation
Let's connect
Professional connections
Connect with me about reliable IT support, endpoint operations, identity administration, and practical security.
zachary.chinn.woo@gmail.comSan Ramon, California